Your bank's software vendor has sent a penetration-test report. Your technology risk team also asks for a source-code review. Are you paying for the same work twice?
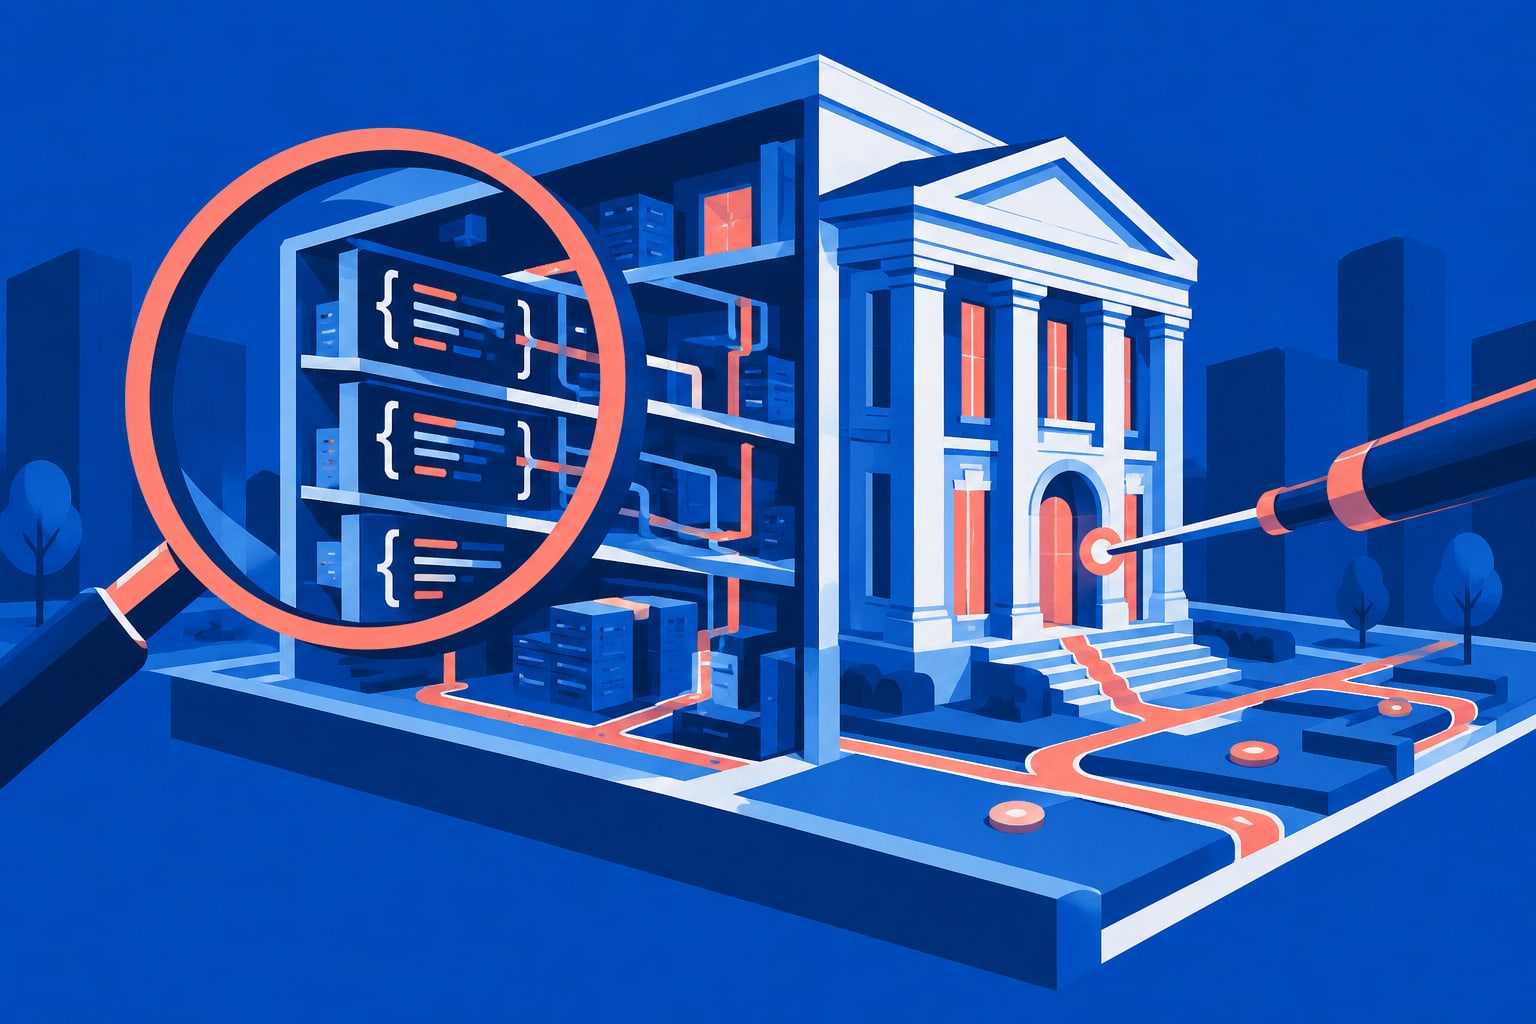
Use source-code review to investigate mistakes in the code. Use penetration testing to investigate whether weaknesses can be exploited in the running application. During software changes, a reviewer can examine how payment-approval rules are written. Before release, a tester can try to bypass those rules in the working system. A bank may need both, depending on its risks.
As the bank application owner, agree the coverage against your application's risks. Then ask your delivery team for results that match the software you plan to release.
What source-code review checks
A reviewer reads the code to understand how the application handles information and decisions. For a payment feature, that could include how it verifies a user's authority to approve a transaction. The review needs context about what the application is supposed to do.
There are two related activities worth separating:
- Manual source-code review: a person examines the code and reasons about it.
- Automated static analysis: a tool analyses code without running the application. Static application security testing, usually shortened to SAST, is the security-focused part of that work.
SonarQube fits the second activity. Its results can help people investigate findings and decide what to fix. Running a scanner does not by itself establish that someone has reviewed the banking rules behind a feature. NIST's Secure Software Development Framework v1.1 treats human code review and tool-based analysis as distinct approaches and calls for findings to be recorded and assessed.
If you are comparing tools, start with our SonarQube Malaysia page or Singapore page. We offer licences, setup and developer training in these markets.
What a penetration test adds
A penetration tester investigates whether weaknesses can be exploited in the application being tested. That brings the running software and its behaviour into the assessment. The tester may have user accounts, architecture details or source-code access, depending on the agreed approach. A penetration test is not always a test performed with no inside information.
The practical distinction is the question being asked:
- Code review: how does this implementation handle the situation?
- Penetration testing: can the tested application be made to behave in an unsafe way?
OWASP's Web Security Testing Guide v4.2 recommends combining testing techniques. It also notes the difficulty of finding runtime errors through source review. Neither technique covers everything on its own.
When commissioning a test, we suggest agreeing the application version, environment, user roles and important business journeys first. Ask what was excluded as well as what was tested.
A payment example: the rule and the running system
Consider a hypothetical payment feature with one rule: the person who creates a payment cannot approve it.
A reviewer could check how the code enforces the approval rule, including other routes through the application.
A penetration tester could use separate test accounts to investigate whether the payment's creator can approve it in the running application.
An automated scanner checks its supported rules.
Give the reviewer and tester the business rule, then ask how each examined it. A green dashboard alone would leave that question unanswered.
How this relates to bank audit in Malaysia and Singapore
Bank Negara Malaysia's Risk Management in Technology policy (RMiT), issued 25 September 2026, requires adequate source-code reviews for changes to critical systems. It addresses independent review and approval of system changes separately. These provisions do not prescribe a particular scanner or say every code review must be an external audit.
Our RMiT source-code review guide explains the requirements and supporting records in more detail. Keep that regulatory review separate from choosing which test answers a particular technical question.
For Singapore, the Monetary Authority of Singapore (MAS) publishes Technology Risk Management Guidelines covering secure coding, source review and application-security testing. The guidelines cover several application-testing techniques. They also discuss testing business logic and tracing requirements to test cases. These are guidelines; confirm the obligations and testing scope applicable to your institution.
Agree the testing scope before the release
Ask which code version, environment, user roles and business journeys each assessment covers. Have the team explain exclusions, unresolved findings and any retesting. For the delivery record and acceptance questions, use our software vendor handover checklist.
If AI tools produced some of the code, our guide to who reviews AI-generated code covers the review responsibilities.
Frequently asked questions
Can a penetration test replace source-code review?
Not automatically. The activities examine software in different ways. Agree their scope against your application risks and applicable requirements. OWASP recommends a combination of techniques rather than relying on one method.
Is a SonarQube scan the same as a manual code review?
No. SonarQube provides automated static analysis. A manual reviewer examines the implementation with context about its intended behaviour. Use scan findings to support that work; do not assume they prove that banking rules were reviewed.
Does a clean report mean the application is secure?
No report establishes that every possible weakness is absent. Read the result against the code, environment and checks in scope. Source review and penetration testing each have limits.
Does BNM require a particular source-code scanning product?
No particular product is prescribed by the RMiT provisions discussed here. The requirement is about adequate review of critical-system code changes; automated tooling appears in separate guidance. Your institution must decide how to meet its obligations.
Can Anchor Sprint help us introduce SonarQube?
Yes. We offer SonarQube licences, setup and developer training, with RM quotes for Malaysia and SGD quotes for Singapore. Tell us your application languages and how your team releases changes so we can discuss the scope.
Discuss your code-analysis setup
Tell us which application you want to start with, its programming languages and where you need help. We can discuss SonarQube setup and training, then quote the licence and services separately. Start with the Malaysia quote route or Singapore quote route.
您的本地 Sonar 经销合作伙伴
向本地合作伙伴购买 SonarQube,以令吉或新元计价
请告诉我们采购公司、新购或续订,以及您需要哪些帮助。
- 马来西亚提供马币报价,新加坡提供新币报价
- 设置协助,单独报价
- 按团队需要提供开发人员培训
Sources
- OWASP WSTG v4.2 introduction: review, penetration testing and a balanced approach.
- NIST SSDF v1.1: code review, analysis, executable tests and release evidence.
- BNM RMiT, September 2026: Malaysian regulatory context.
- MAS TRM Guidelines: Singapore supervisory guidance.
- SonarQube Server static-analysis and Advanced Security overview: tool scope.
References and service scope checked on 17 October 2026. Confirm the regulatory context with your institution's relevant reviewers.