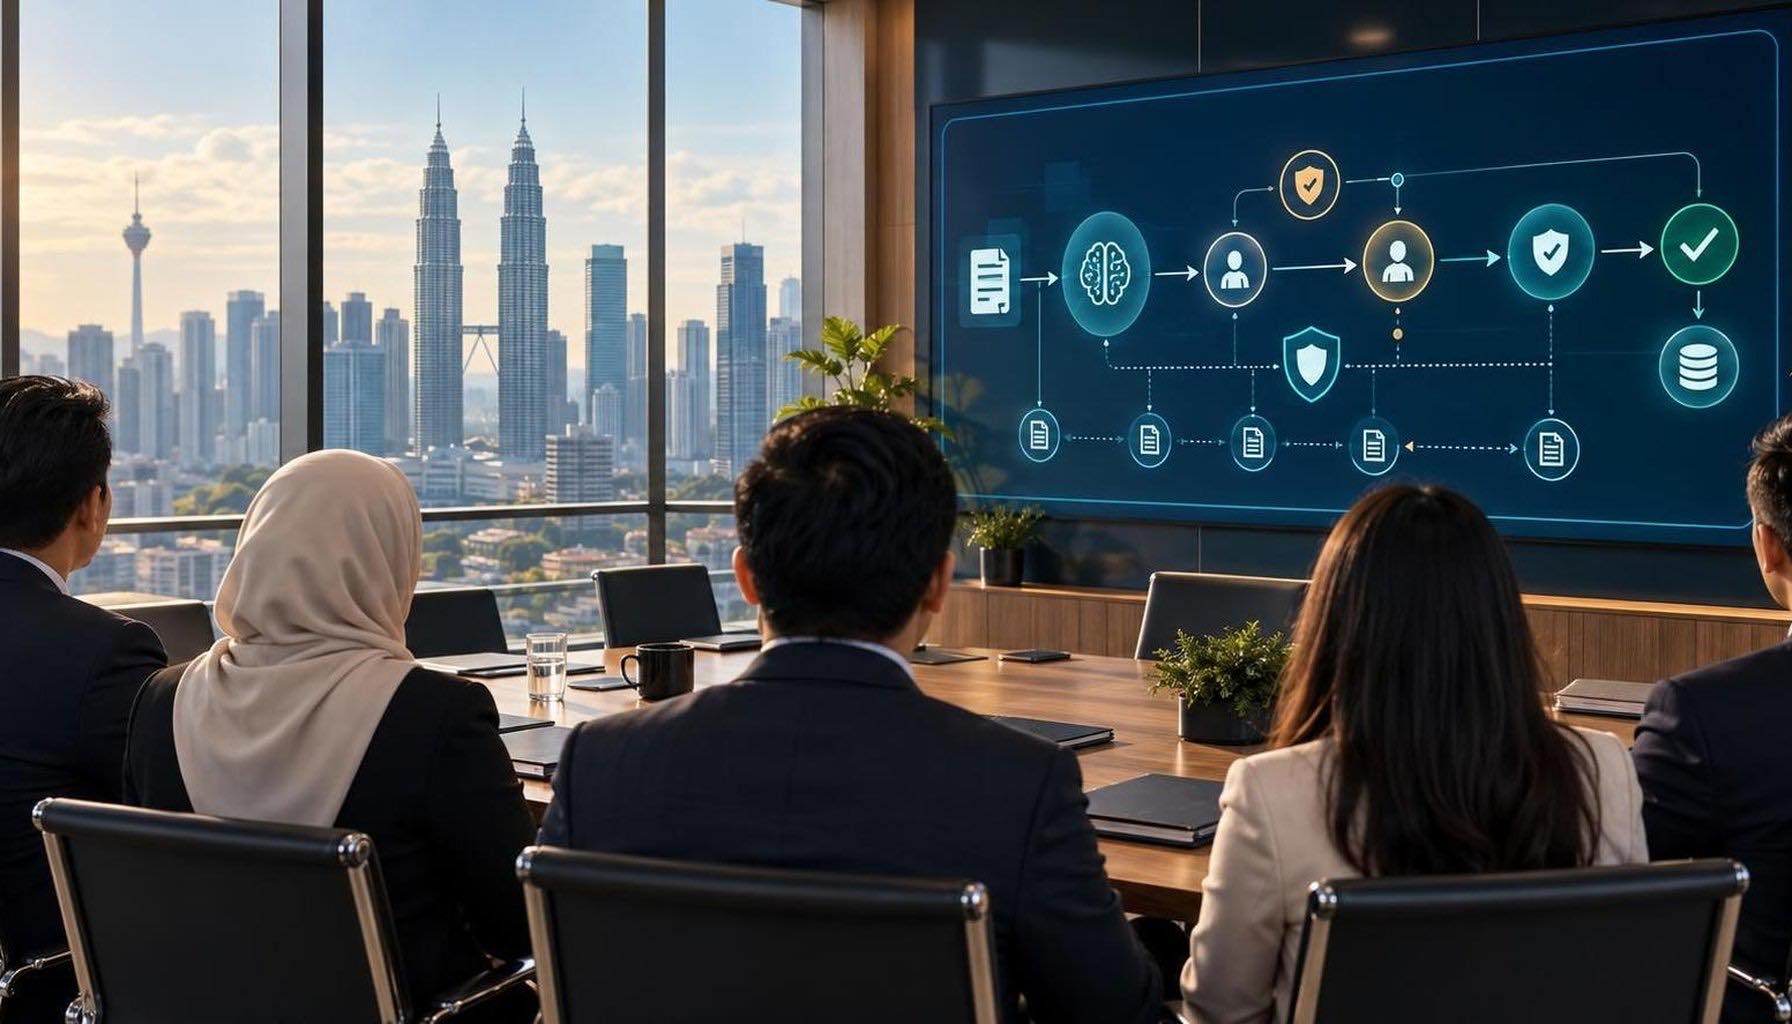
It is Monday morning at a growing firm in Penang. Sales staff use generative AI to draft proposals, HR has tested it to screen CVs, and customer service uses an automated tool to route complaints. Then a director asks which AI tools are in use, what data they take, and who is in charge when they get something wrong.
Many firms cannot give a clear answer. That governance gap now needs attention. The Government sought public views on the proposed Malaysia AI Governance Bill from 10 July to 1 August 2026. The proposal points to central oversight, shared principles, and duties that rise with risk for both small firms and large groups.
This does not mean you should stop useful AI work, but AI can no longer stay hidden in small tests across your organisation. You need an inventory, a named owner, an assessment of possible harm, and evidence of the controls you use.
Malaysia plans a wider set of AI rules
The proposed Bill would be Malaysia's first broad law for AI governance. This broad framework could apply across many fields. It would support rather than replace current laws. Those laws already cover personal data, employment, finance, and consumer dealings.
The Ministry of Digital says duties may follow an AI system from its first design through to the day it is retired. The plan also covers safeguards, incident reports, and supervised test spaces known as regulatory sandboxes.
This turns responsible AI from a broad goal into a daily duty. A policy may promise careful use, but that claim means little if no one can identify the tool involved. Your organisation should also show why it accepted an output, what a person reviewed, and how it handled an incident.
Malaysia has already set a path for fair, open, and safe AI through the National AI Office's governance work. The proposed law may make each duty clearer. Your key task is to keep a sound record of each decision.
Your role and level of risk will shape your duties
The paper draws a line between developers and deployers. A developer builds an AI system or makes major changes to it. A deployer puts that system to work. Your firm may fill one role or both. Buying a tool trained elsewhere may still leave you with duties as a deployer.
Rahmat Lim & Partners' review of the paper lists five governance principles, three risk tiers, and functions for a Central AI Authority. The key point is that duties may differ by use. Checks should grow as the possible harm rises.
This is why you should rate each use by the harm it may cause. A tool that cleans up meeting notes poses less risk than one that helps choose who gets a job or loan. The same applies in health care and essential services, so assess the purpose, data, affected people, and consequences of a wrong result.
The consultation review also makes clear that your duty lasts while you set up, use, check, change, and retire the system.
Start these four records before the law is final
The Bill remains a proposal and its final duties may change, but you can build a useful foundation without a large compliance team.
1. Create a working AI register
Create one shared register of every AI use you can identify. For each entry, note the tool, purpose, owner, users, and data. Add the provider, system links, and last review date. Include free accounts, AI features inside other software, and department pilots.
Ask finance about paid tools and IT about approved apps. Ask team heads about pilots and staff about personal accounts. Keep the register current as the business changes; it is not a one-off audit file.
If you are still choosing where AI fits, our AI adoption roadmap for Malaysian businesses shows how to sequence use cases before adding more tools.
2. Give every use case a named owner
The owner should understand the business process. That person does not always sit in IT. IT can manage access, safety, and links to other systems. Yet HR should own an AI hiring process, while finance should own invoice approval.
Record who approves the tool and who checks it. Also name the person who can pause it. The owner should start a new review when the seller changes the model. Do the same when a team expands its purpose. This makes responsible AI part of normal management, not an annual policy exercise.
3. Classify risk using consequences
You do not need to guess the Bill's final legal tier for each tool. Begin with a simple check of your own. Ask whose rights or access may be affected. Check for private or sensitive data. Then ask how a person can challenge the output and how serious an error could be.
A low-impact writing tool may need approved-use rules and basic checks. A tool that ranks candidates, changes prices, detects fraud, or approves a customer request needs stronger controls. Such uses need strong tests and senior approval. They also need checks by staff and close review. Classify the risk again if the purpose changes.
The technical design also matters for sensitive data. Our guide to private LLM deployment and enterprise data privacy explains when tighter control over data and infrastructure may be justified.
4. Preserve evidence while the work happens
Do not wait for an inquiry before you work out what an AI tool did. Keep the tool version or seller, test cases, approval notes, and staff guides. Add known limits, review results, and records of harm. For higher-risk uses, record when a person overrode the AI and why.
You do not need a new platform on day one. A safe folder, one review form, and a change log may be enough for a smaller business. Update them consistently so the records show a clear decision process rather than paperwork with no purpose.

Put the rules inside the live system
AI rules can fail when they sit apart from the live system. A policy may require human approval, while the live process sends output straight to a customer record. A team may promise incident logs while its tool keeps no useful history.
Build checks into the design. Use access limits, approval steps, logs, backup plans, and a clear stop switch. A confidence limit can send uncertain results to a person. This matters most when AI reads from or writes to your CRM, ERP, document store, or customer channels. System integration is where policy must turn into real checks.
The same discipline helps a successful pilot become a stable live tool. Our report on why Malaysian AI pilots stall covers the gaps in ownership, oversight, and integration that often appear after a good demo.
Plans for faults should match the risk. State what counts as a fault and who gets the report. Set out what proof to keep and when to stop the tool. The Ministry's plan supports reports and safeguards, while regulatory sandboxes may offer supervised tests for new uses.
Keep useful work moving through a clear gate
The proposed Malaysia AI Governance Bill should change the order of your work, not stop it. Before a new use goes live, review its register entry, owner, risk rating, and control evidence.
Low-risk tools can pass through a light gate, while high-risk tools need deeper tests and clear approval. This lets staff gain value from AI without leaving important work ownerless or hard to audit.
If you plan a new tool, our AI solutions team can turn governance needs into practical system controls, including human review, logs, access rules, and a safe stop process.
The firms best prepared for Malaysia's AI law may not have the longest policy. They will have a current register and a named owner for each tool. They can explain each risk decision and show what happened in practice. You can start building that evidence this week.
Konsultasi percuma
Make Your AI Projects Governance-Ready
Map your AI use cases, risk controls and evidence before regulation catches up with deployment. We help Malaysian businesses build practical governance into real systems.