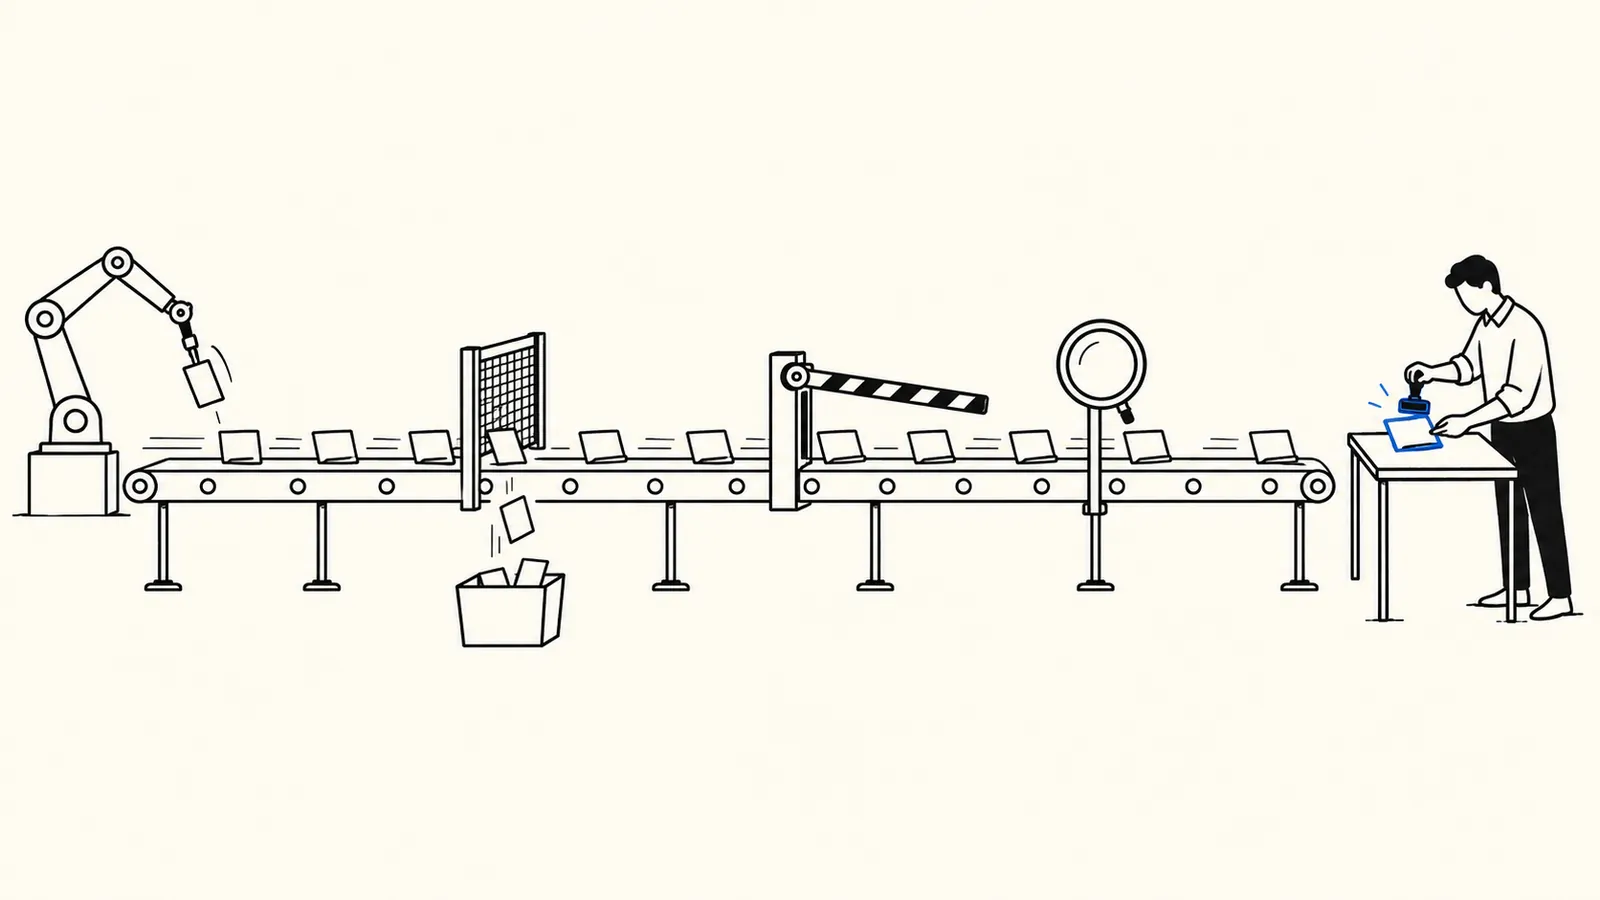
Several checks read the code first. One person signs it off.
Picture an engineering lead at a fintech in Kuala Lumpur on a Monday morning. Over the weekend, three coding agents opened 40 pull requests. Two people on the team can approve them, and both have their own work.
So who reviews AI-generated code when agents write faster than people can read? A stack of checks does most of the reading, each catching a different kind of mistake. A person signs off at the end.
Each layer below names the Sonar product that does the job and the plan it needs, as of October 2026. If you lead engineering in Malaysia or Singapore, including at a bank or fintech, this is the order we would set it up in.
Agents now write faster than people can review
In Sonar's own 2026 survey of 1,149 developers who had used AI at work in the past year, AI accounted for 42% of committed code. The survey says that share is expected to reach 65% by 2027. The same survey found 96% "do not fully trust AI-generated code", and "only 48% always verify it before committing".
Review is where the work piles up. In that survey, 38% said reviewing AI code takes more effort than reviewing a colleague's. GitHub reported in May 2026 that "More than one in five code reviews on GitHub now involve an agent".
Many agent pull requests show no sign of review at all. A 2026 study of agent-written pull requests in popular GitHub repositories found 61.38% had "no recorded review activity". Of the review comments that did exist, 71.58% came from agents.
GitHub's 2025 Octoverse report shows the same shape. Merged pull requests rose 23% in a year, while comments on issues and pull requests stayed "essentially flat". GitHub calls these observational signals, not proof of cause.
What slips through when nobody reads the diff
Four kinds of problem matter most when an agent writes the code.
- Dependencies the agent pulled in. Sonar warns that "agents may autonomously install packages without manual vetting". A 2025 study found AI models invent package names that do not exist: on average at least 5.2% of suggested packages for commercial models, and 21.7% for open-source ones.
- Injection. Sonar recommends checking AI code to "eliminate injection vulnerabilities", such as user input pasted into a database query. Agents face a second kind too, called prompt injection.
- Secrets. GitGuardian's 2025 report found that public repositories using GitHub Copilot had a 6.4% secret leakage rate. That was 40% higher than the average public repository.
- Business-logic and access-control flaws. Broken access control is number one in the 2025 OWASP Top 10, a widely used list of web application risks from the Open Worldwide Application Security Project. In the data behind that list, 100% of the applications tested had some form of it.
Invented package names are a real attack route. The study's authors call them "a novel form of package confusion attack": whoever registers that name first decides what your build installs.
Prompt injection is the risk agents add on top of ordinary code flaws. OWASP warns that indirect prompt injection happens when a large language model (LLM) "accepts input from external sources, such as websites or files". In our view, that means an agent reading a poisoned issue or README could be steered.
For our money, access-control flaws are the hardest of the four. The code does exactly what it says and passes its tests. It just lets the wrong person do it.
Six checks, in the order agent code meets them
We group the stack into six checks. Sonar's own framework sorts its products into three loops:
- While the agent writes (the agentic loop).
- At the pull request, before anything merges (the CI, or continuous integration, verification loop).
- Across the codebase, after merge (the code maintenance loop).
You can cover some layers with other tools. Branch protection in your Git platform handles approval, for example. We map the six checks to Sonar because one vendor covers each of them, and because we resell it.
Back to the 40 pull requests. Here is what each layer would do with them, and the plan it needs.
1. While the agent writes: Sonar Vortex
Sonar Vortex gives a coding agent your project's context "before they write a line of code, then verifies their output in real time". It works with Claude Code (Claude, powered by Anthropic), Codex, GitHub Copilot CLI, Cursor and Antigravity, among others. Sonar says it "works alongside your existing CI", not instead of it.
This is the earliest place to catch a mistake, before any of the 40 pull requests exists. In Sonar's own test with one coding agent, Vortex cut the issues the agent produced by 92%. That figure is Sonar's own; we have not seen an independent test.
Plan. On SonarQube Cloud, Vortex comes in Sonar Agent Essentials, which needs the Enterprise plan or an annual Team plan. On SonarQube Server, it is a separate subscription for the Enterprise edition, version 2026.5 or later.
2. On the pull request: Gitar, the AI reviewer
Gitar is an AI pull request reviewer that Sonar acquired on 21 May 2026. When a pull request opens, it "automatically reviews the code and posts inline review comments along with suggested fixes". On Monday, that means each of the 40 has a first-pass review before a person opens it.
When a CI run fails, Gitar works out why and "suggests a fix, which it can commit automatically or on demand". Sonar's pricing page lists a loop that "iterates until CI passes" as a Pro plan feature.
That changes who wrote the pull request. Once Gitar commits, the change has two AI authors: the agent and the reviewer. A person still has to approve it.
Plan. Gitar is a separate Sonar product that "can be purchased separately". It is priced per user on its Core and Pro plans, and Enterprise pricing is custom. When Sonar bought Gitar, it said Gitar would also be available to buy with SonarQube and SonarQube Advanced Security.
3. At the merge: the quality gate
An AI reviewer gives an opinion. A quality gate is a pass or fail check with written conditions, and it can block the merge.
SonarQube AI Code Assurance holds AI-written projects to a gate built for them. Our guide to SonarQube AI Code Assurance and the quality gate for AI-generated code explains its six conditions and setup, so we won't repeat them here. Of the 40, any pull request that breaks the gate's conditions can be held back from merging, once the gate is set as a required check.
Plan. On SonarQube Server, pull request analysis, merge blocking and AI Code Assurance start at the Developer edition. The free Community Build analyses only the main branch.
4. Dependencies: SonarQube Advanced Security
Advanced Security checks the open-source packages your code uses. It flags known vulnerabilities, and its reachability analysis ranks the ones "your code actually calls" first.
It also checks dependencies "against known malicious packages". Licence policies are covered too. For audits, it exports an SBOM (software bill of materials, a list of every component you ship) in CycloneDX and SPDX, two widely used formats.
For the 40 pull requests, this is the layer that checks each package an agent added against vulnerability and malware lists, and against your licence policy. A brand-new malicious package may not be on any list yet, so a person should still question any dependency nobody asked for. Without Advanced Security, the dependency condition in Sonar's AI quality gate is greyed out and skipped.
Plan. A separate subscription on the SonarQube Cloud Team and Enterprise plans, and on SonarQube Server Enterprise.
5. Across the codebase: SonarQube Hunter Agent
The Hunter Agent looks for "broken access control, business logic, and authentication flaws that traditional analysis misses". Sonar's launch announcement says it runs in the background, on a schedule or on demand, so it "never blocks a pull request".
Sonar's documentation is clear that it "doesn't fix the issues it finds". It scans the merged codebase, so it sees the 40 together after they land. Someone still decides what each finding means for your business.
Plan. A separate subscription. On SonarQube Cloud it needs the Enterprise plan. On SonarQube Server it needs the Enterprise edition, version 2026.5 or later.
6. Fixing at scale: AI CodeFix and the Remediation Agent
AI CodeFix uses an LLM to suggest a fix for an issue SonarQube has found. Developers see the suggestion in SonarQube or their editor and choose whether to apply it.
The SonarQube Remediation Agent goes further: it proposes fixes and opens new pull requests for your team to review. It works on your backlog and on pull requests that fail the quality gate.
On SonarQube Cloud, the pull request part works only for projects connected to GitHub. For the 40 on Monday, a pull request the gate held back may get a proposed fix as a new pull request, if its language is supported and the fix passes Sonar's re-check.
Fixes that fail Sonar's re-check are not shown to you. And it never merges: "Your developers do".
One detail matters for regulated teams. Sonar says running SonarQube Server on your own infrastructure "does not keep code within your network when you use the agent". The code goes to the LLM provider your administrator sets up, such as Azure AI Foundry or AWS Bedrock.
Plan. AI CodeFix is available on SonarQube Server Enterprise and the SonarQube Cloud Team and Enterprise plans. On SonarQube Cloud, the Remediation Agent comes in Sonar Agent Essentials, with an annual Team plan or the Enterprise plan. On SonarQube Server, you buy it separately for the Enterprise edition, version 2026.5 or later.
What still needs a human
Every layer above narrows what a person has to read. None of them owns the decision to ship.
Approval
As of October 2026, GitHub's documentation says pull requests from its Copilot cloud agent "must be reviewed and merged by a human". The agent "cannot approve or merge a pull request". GitHub also stops the person who asked the agent for the change from approving it.
Anthropic's documentation for Claude Code GitHub Actions advises: "review Claude's changes before merging". Our guide to running Claude Code as a team covers that setup. Either way, treat any AI reviewer, Gitar included, as a reviewer that comments, not one that approves.
Segregation of duties
Write the rule down. Whoever approves an agent's pull request must be someone else: not the agent that wrote it, and not the person who asked for it.
For Malaysian banks and insurers, Bank Negara Malaysia's Risk Management in Technology policy (RMiT) asks for procedures "to independently review and approve system changes". It also asks for "appropriate segregation of duties throughout the SDLC", the software development lifecycle. Our RMiT source code review guide maps those clauses to the evidence auditors ask for.
In Singapore, the Monetary Authority of Singapore (MAS) publishes Technology Risk Management Guidelines (January 2021). They ask financial institutions to "adopt standards on secure coding, source code review and application security testing". The guidelines also say major issues "should be remediated before production deployment". Our SonarQube Singapore page maps the relevant Technology Risk Management (TRM) paragraphs to the SonarQube features that support them.
If you handle card payments, the Payment Card Industry Data Security Standard (PCI DSS) v4.0.1 lets you review code "using either manual or automated processes" (requirement 6.2.3). Whether an assessor accepts an AI reviewer as that automated review is not settled, so ask yours first. Treat this section as a starting point for your compliance team, not legal advice.
Design review
No tool in this stack knows whether the change should exist at all. A short design review before a large agent task starts should answer questions like these:
- Does the change match what the customer asked for?
- Does it add a second way of doing something the codebase already does?
- Should a refund over RM 50,000 need a second approver?
Ask them before the 40 pull requests arrive, not after.
How to start: which plan, and a checklist
Most teams do not need every layer on day one. Here is a sensible order.
- Turn on pull request analysis and merge blocking. On SonarQube Server this needs the Developer edition or above; our edition comparison shows what each adds. On SonarQube Cloud, the Team plan analyses every pull request. Without this, agent code reaches main before SonarQube checks it.
- Label AI-written projects and apply the AI quality gate. Follow the setup checklist in our AI Code Assurance guide.
- Require a human approval, and block self-approval. The person who asked the agent for a change should not approve its pull request.
- Add Advanced Security if agents are allowed to add packages.
- Add Gitar if reviewers are drowning in pull requests, so the first pass and CI fixes happen before a person looks.
- Add the Sonar agents when the backlog justifies them. As of October 2026, they are paid add-ons. On SonarQube Cloud they need an annual Team plan or the Enterprise plan, and the Hunter Agent needs Enterprise. On SonarQube Server they need the Enterprise edition, version 2026.5 or later. For how SonarQube itself is priced, see our guide to SonarQube pricing by lines of code.
- Decide where your code may go. SonarQube Cloud stores data in the EU or the US only. If code must stay in-house, use Server, and check which LLM endpoint the Remediation Agent and any other LLM-backed feature will call.
- Review after a month. Tag agent pull requests by author or label so you can count them. Then count how many merged with no human comment. That number should fall.
Frequently asked questions
Who should review AI-generated code?
Several automated layers, then a person. Scanners and an AI reviewer catch known patterns, and a quality gate blocks the merge on written rules. A human approves, and it should not be the person who asked the agent for the change.
Who is responsible for code an AI agent writes?
In practice, the people who ask for it and approve it share that responsibility. The Claude Code documentation tells the person using the tool: "You're responsible for reviewing proposed code and commands for safety before approval". Who owns the copyright, and who carries legal liability, are separate questions for your counsel.
Which SonarQube edition do we need to review agent code?
As of October 2026: on SonarQube Server, pull request analysis and the AI quality gate start at the Developer edition. AI CodeFix needs Server Enterprise or a Cloud Team or Enterprise plan. The Remediation Agent and Hunter Agent are separate subscriptions, and the Hunter Agent needs the Cloud Enterprise plan or Server Enterprise 2026.5 or later.
Is Gitar part of SonarQube?
As of October 2026, it is a separate Sonar product that can be bought on its own. Core and Pro are priced per user, and Enterprise pricing is custom. When Sonar acquired Gitar, it said Gitar would also be available to buy with SonarQube and Advanced Security.
Do Sonar's agents keep our code on our own servers?
Not entirely. Since version 2026.5, Sonar's agentic capabilities are available on self-managed SonarQube Server. But Sonar says the Remediation Agent still sends code to the LLM provider you configure.
Rakan kongsi penjual semula Sonar tempatan anda
Beli SonarQube daripada rakan kongsi tempatan, dalam Ringgit atau SGD
Anchor Sprint ialah rakan kongsi penjual semula Sonar di Malaysia dan Singapura. Hubungi kami tentang lesen SonarQube Cloud atau Server, Advanced Security, Gitar dan ejen AI, pembaharuan, atau semakan percuma tentang keperluan pasukan anda.
- Sebut harga dalam Ringgit (RM) atau dolar Singapura (SGD)
- Persediaan tempatan pada repositori dan CI/CD anda
- Latihan pasukan, boleh dituntut HRD Corp di Malaysia
Sources
- Sonar documentation: Agent Centric Development Cycle (Vortex, Remediation Agent, Hunter Agent, AI CodeFix), checked 7 October 2026.
- Sonar: Sonar acquires Gitar, 21 May 2026, and the Gitar plans page.
- GitHub Docs: Copilot cloud agent risks and mitigations, checked 7 October 2026.
- Spracklen et al., package hallucinations by code-generating LLMs, USENIX Security 2025.
- Bank Negara Malaysia, Risk Management in Technology, issued 25 September 2026.
See SonarQube in Malaysia, including Gitar and the AI agents, or SonarQube in Singapore if you buy there.